South Korea's President Lee orders review of a government-wide cybersecurity body
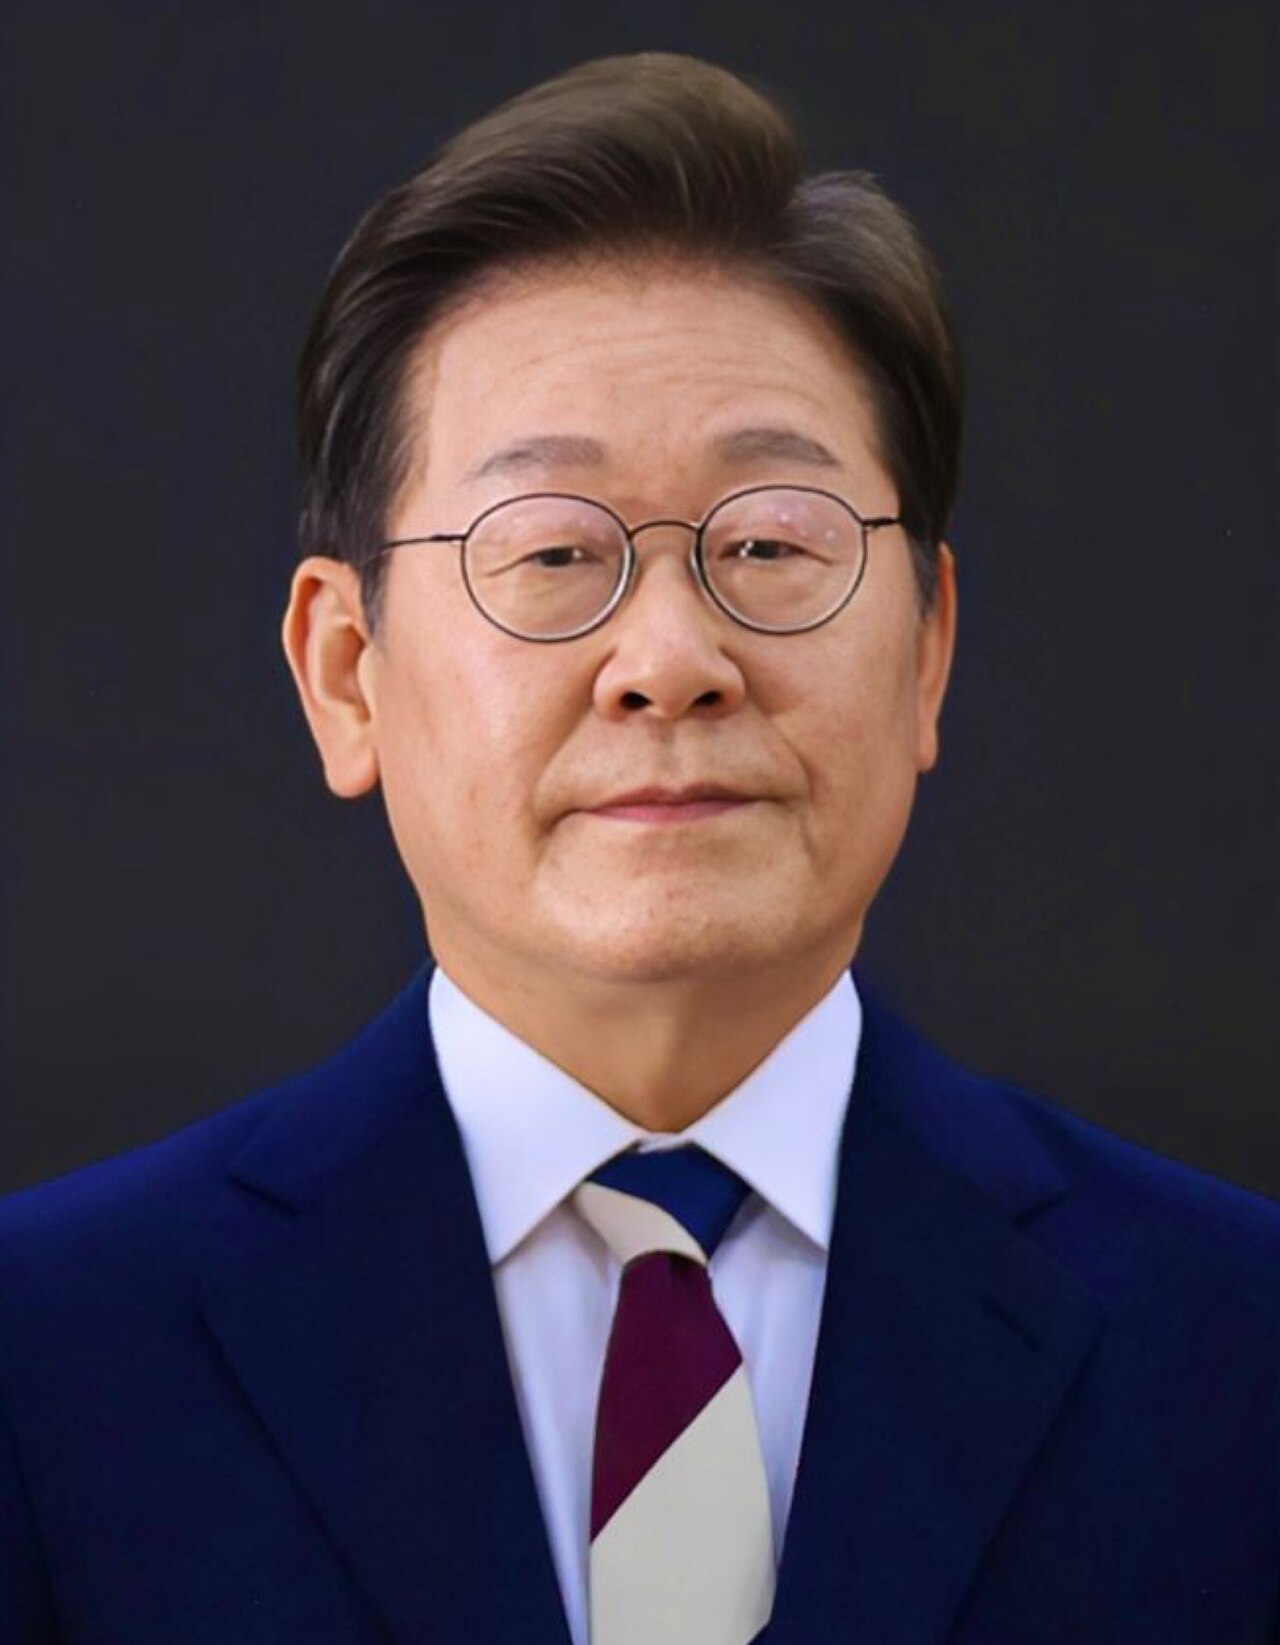
South Korean President Lee Jae Myung told a Cabinet meeting on November 3, 2026, that officials should consider a powerful government-wide cybersecurity body to coordinate security functions now scattered across agencies, Reuters and Korean outlets reported. No decision on the form of the body had been reported as of this record.[1][2]
What Lee said
At a Cabinet meeting he chaired at the Blue House, Lee said the existing security system, centred on inspections and after-the-fact responses, was showing clear limitations. He asked officials to consider a cybersecurity tsar body that could oversee and coordinate scattered security functions, and said a government-wide task force spanning the public and private sectors should also be discussed.[2][1]
Lee said the country must build a system that can respond in advance to signs of attacks, and that it needs world-class cybersecurity capabilities along with semiconductors and AI. The Korea Times reported that he called for stronger protection of telecommunications, energy and finance infrastructure.[2][3][4]
The attacks behind the remarks
Reuters reported that South Korea's financial sector had been hit by attacks in recent weeks. It reported that Lee referred to the theft affecting the Binance cryptocurrency exchange without directly naming North Korea, which the FBI has blamed for that attack, and that North Korea denied involvement. Seoul Economic Daily said the remarks appeared to refer to an unauthorized withdrawal of $6.3 billion in cryptocurrency from Binance on October 29.[1][3]
Inspections under way
The Korea Times, citing reports, said the National Intelligence Service asked more than 2,100 central and local government bodies on October 22 to inspect their systems with a security checklist, and that the NIS is separately inspecting internet-connected systems at key public infrastructure. The paper reported that the Ministry of Science and ICT is checking about 170 major private-sector facilities, and that cybersecurity duties are currently split among several agencies.[4]
Expert views
Youm Heung-youl of Soonchunhyang University told The Korea Times it needs to be discussed whether Lee means an agency established by law or a committee, and said what matters most is that the body has real authority. Hwang Suk-jin of Dongguk University said self-assessments by financial companies can miss actual vulnerabilities or become a formality.[4]
The record
- Event type
- Official action or statement[1]Stated by Reuters, official account, Nov 3, 2026
- Means
- None[1]
- Target type
- Government facility[1]
- Occurred, start
- Nov 3, 2026[1]Stated by Reuters, official account, Nov 3, 2026
- First reported
- Nov 3, 2026The date of the earliest cited source
- Primary place
- Cheong Wa Dae, Seoul (site)[2]Stated by The Kyunghyang Shinmun, official account, Nov 3, 2026
Each value is what a cited source stated, with its source number. Where sources give different figures, the latest official account is listed first and every other figure is listed with it. A figure for one part of an event, such as one strike in a campaign, is listed as that part and never as the total.
Case and outcome record
| Date | Stage | Who | Court, office or agency | As the source states it |
|---|---|---|---|---|
| Nov 3, 2026 | Incident | South Korean Cabinet meeting | President called for creation of a powerful government-wide cybersecurity body[1] |
One row per stage for each person, as sources report it. A stage a source only expects is not listed until it happens.
IPR records what each source says and who said it. A cited statement shows that a source said it, not that it is true. Hover a number to see the exact words quoted from that source. See something wrong? Use a flag to report it.